

Pimcore
How Pimcore Helps Businesses Manage Multi-Channel Commerce
Nidhi Pandey|Mar 23, 2026|Read 12 Min


PHP released emergency fixes on October 21, 2026, for two critical flaws, CVE-2026-109618 and CVE-2026-109619, known together as PHP2Shell. Most coverage focuses on storefronts, but Pimcore runs on PHP too, and a compromised PIM (Product Information Management, the system that holds and governs product data for every sales channel) puts every channel at risk at once. If your Pimcore server runs an unpatched PHP build, patch it first, then check that your product data is still trustworthy.
PHP2Shell is two use-after-free (a memory bug where software keeps using memory after releasing it, letting an attacker place their own data there) flaws in the PHP runtime, both rated CVSS 9.2 (Critical). They allow remote code execution (an attacker runs their own commands on your server from the internet) without a login. PHP handles each request before Pimcore or Symfony code runs, so no Pimcore update can fix it.
"These findings rank among the most severe vulnerabilities discovered in PHP, and arguably in software history." Wiz researchers, via Help Net Security.
Pimcore usually connects to your ERP and your sales channels, and those connections run on API keys and service accounts stored on the Pimcore server. An attacker who runs code as the web worker account can read whatever that account can read, including those credentials, and use them to reach every connected system.
Channels accept product data from the PIM without question. One altered record can publish wrong prices or specifications to your website, apps and marketplaces at the same time.
Admin interfaces, DataHub (Pimcore’s data delivery layer, which exposes product data to other systems through APIs such as GraphQL) endpoints and import tools are frequently reachable from the internet so partners and agencies can use them.
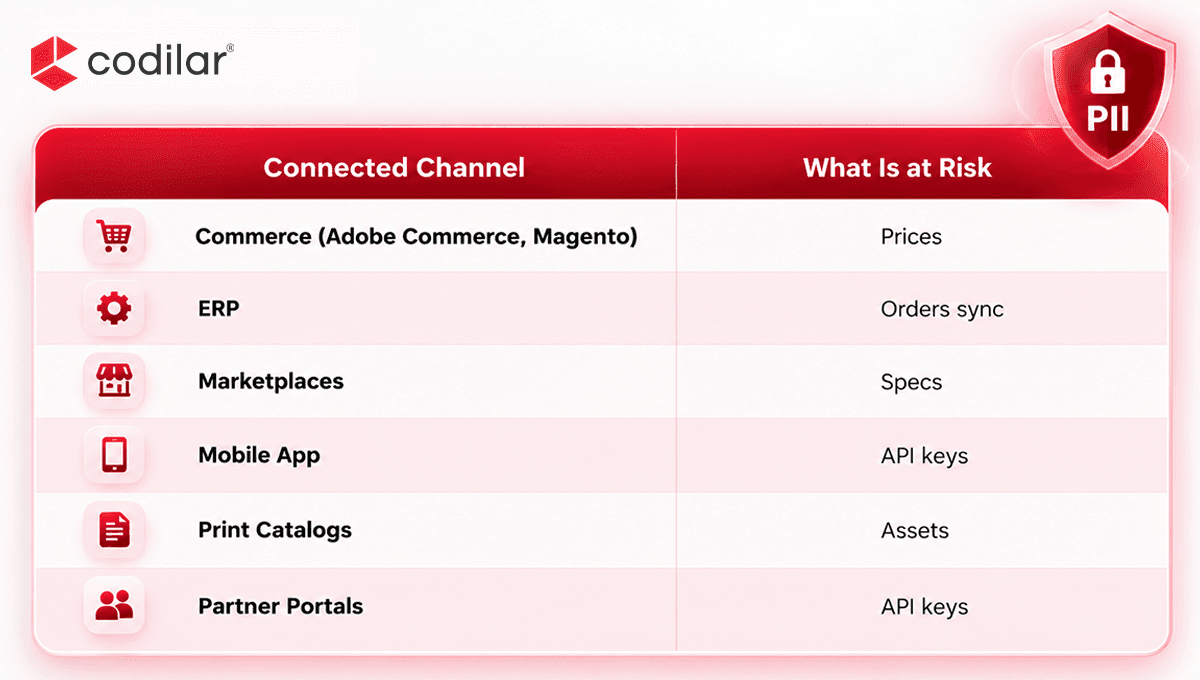
Every channel in this table receives its data from Pimcore, so one breach reaches all of them together. Patch your PIM with the same priority as your storefront.
PHP shipped fixes only for 8.2 and newer. PHP 8.1 and older get no official release, just source backports someone has to build and test.
Per Pimcore's system requirements:
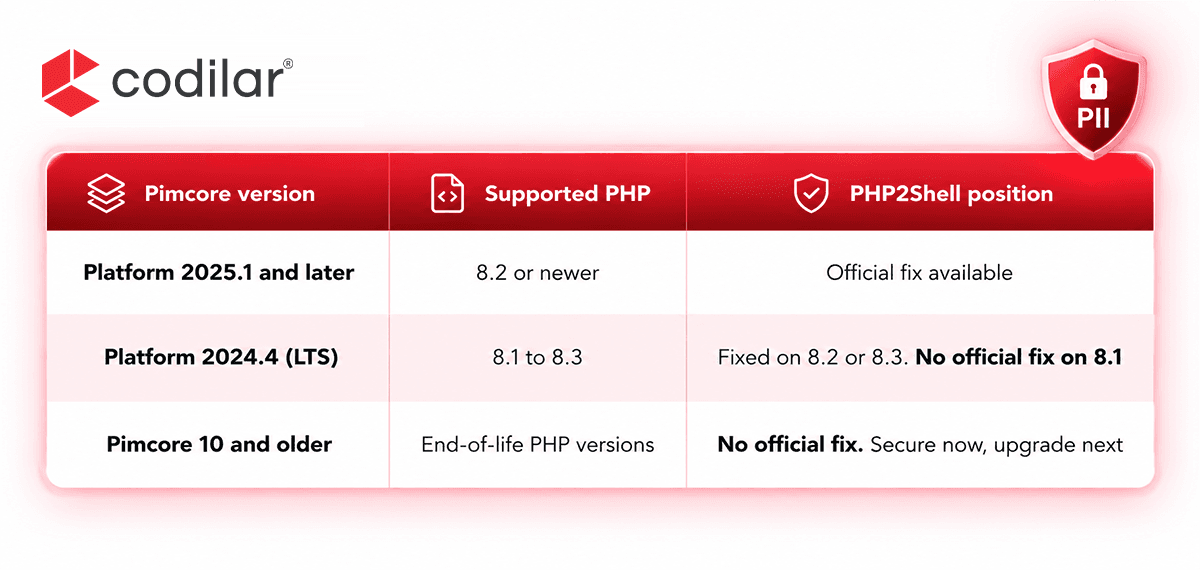
Platform 2024.4 is supported until December 2026, so even fully patched LTS installs need an upgrade plan.
On PHP 8.1, secure Pimcore within its current PHP version through a tested backport and hardening, then upgrade Pimcore onto supported PHP.
Check through the web server, across production, staging and any import or worker servers.
Move to 8.5.12, 8.4.27, 8.3.36 or 8.2.35, or a tested backport, then restart PHP-FPM or Apache. Pimcore supports both, and Apache with mod_php carries the highest risk.
Docker-based installs
A container keeps the PHP version it was built with, so updating PHP on the host changes nothing inside it. Rebuild every image from a patched base and redeploy it, including worker containers (background processes that handle imports and scheduled tasks). Then confirm the PHP version a running container serves, as in step 1.
What not to rely on
WAF rules alone or "it's only an internal tool". Attackers are already adapting payloads to evade WAF rules.
Test imports, DataHub endpoints, workflows, ERP sync and channel exports before closing the incident.
Amazon's honeypots recorded an exploit attempt on 17 October, four days before the fix. No breach had been publicly confirmed at the time of writing, which doesn't mean none happened.
Review activity from 17 October for:
Use Pimcore's version history to compare recent changes to prices, specifications and compliance fields against your ERP or source data.
Rotate ERP service accounts, commerce and marketplace API keys, DataHub keys and database passwords.
Pimcore already has strong integrity tools.
The task is to use them deliberately:
Where Pimcore holds customer or partner data, field-level encryption (encrypting individual sensitive fields, such as a name or an email address, inside the database) means a copied database shows encrypted records, not identities. We built this approach for commerce as PII Shield and engineered it for Pimcore where needed.
Start with a free PHP2Shell Exposure Check, run read-only and with your written consent, with findings in 48 hours. Where action is needed, we patch PHP or secure Pimcore within its current PHP version, targeting 48 hours for standard environments.
Compromise sweep, product data integrity review, credential rotation and permission hardening.
A move to a current Pimcore Platform release on supported PHP, cleaner integrations and managed DevOps.
Your PIM is the one system every channel trusts. After PHP2Shell, prove that trust is still deserved.❞

Venugopal C | Solution Architect
Pimcore sits at the center of your commerce operation, so it deserves the same security urgency as your storefront. Update PHP, then check that your product data and integrations are clean. Monitoring lets you act on the next vulnerability the day it is announced. Book a free security check and we will review your PHP version and your Pimcore setup together.
Running another PHP platform? Read our guides for Adobe Commerce, Magento and custom PHP.
Yes. Pimcore runs on PHP, and PHP2Shell affects every PHP installation serving web requests, whether through PHP-FPM or Apache mod_php. The flaw sits in the PHP runtime, which handles requests before Pimcore code runs, so every Pimcore install needs a patched PHP version or a tested backport.
No. Pimcore and Symfony updates don't change the PHP runtime. You need PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35, or a vendor backport for older versions, followed by a restart of every PHP worker and a rebuild of any containers.
If you run PHP 8.2 or 8.3, update to the patched release and restart workers. On PHP 8.1, apply a tested backport now. Either way, plan an upgrade: 2024.4 is supported until December 2026, and later releases require PHP 8.3 or newer.
It's possible if your server was unpatched after 17 October. Use Pimcore's version history to compare recent changes to prices, specifications and compliance fields against your ERP or source data, and check admin users, roles and DataHub configurations for anything unfamiliar.
Rotate ERP service accounts, commerce and marketplace API keys, DataHub keys, database passwords and any third-party tokens stored on the Pimcore server. The second PHP2Shell flaw can leak secrets from memory, so assume anything in use during the exposure window could be known.
Get tailored technology solutions to scale your retail business online
Request A Quote
Stay ahead with insights, trends, and brand success stories from the world of Digital Commerce.


With world's leading digital commerce agency.